UtoczkiShare
A secure photo sharing and management platform built with Django and React, featuring strict, user-scoped access control. Built as the qualifying task for the Hack4Defence 2025 hackathon.
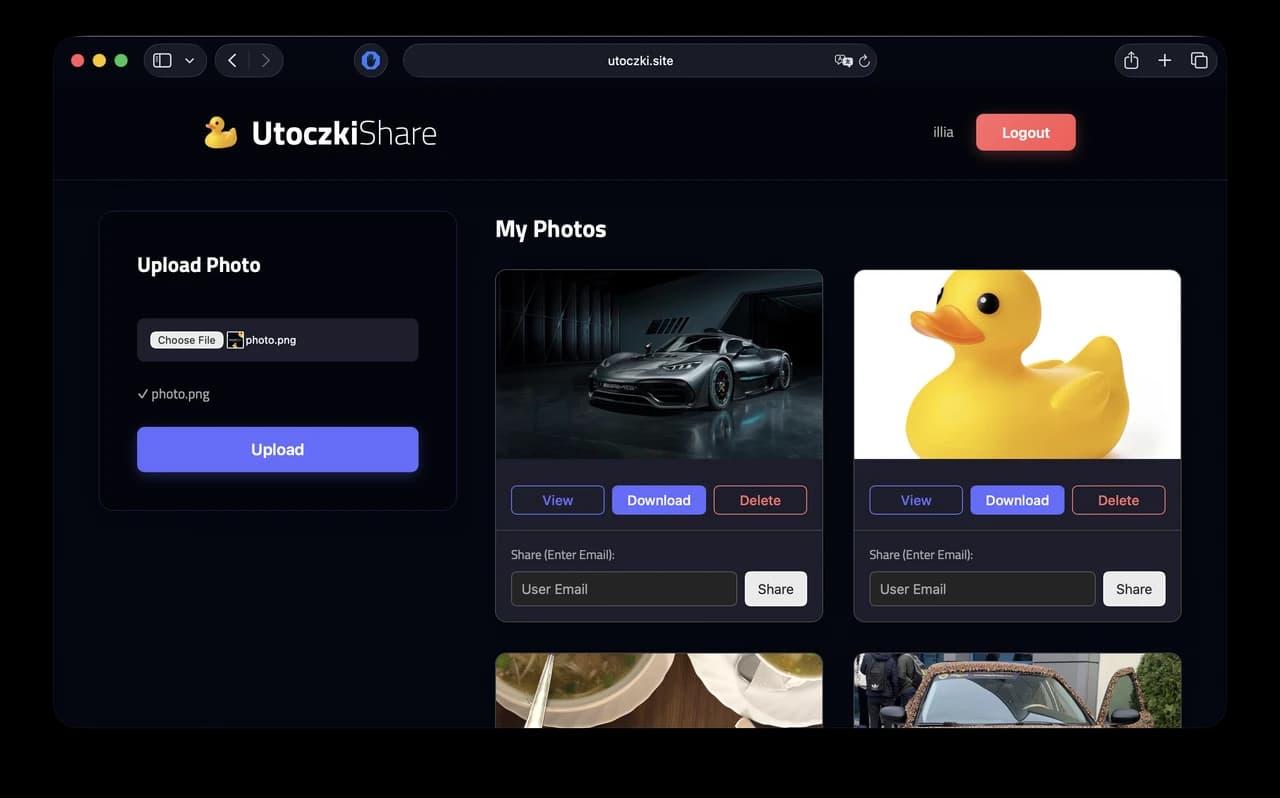
People register, upload photos and share individual photos with other accounts by email. The gallery combines photos a person owns with photos shared to them.
The qualifying task prioritized security, so the work centres on who may read which file.
- Does the requester own this photo?Yes: 200, the file
- Does a PhotoShare link them to it?Yes: 200, the file
- Neither403 Forbidden
Every file goes through a permission check
Media is served from a protected endpoint, /api/media/. It returns the file only if the requester owns the photo or a PhotoShare record links them to it, and 403 Forbidden otherwise.
IDOR protection by scoping
Endpoints for viewing, deleting and sharing are scoped to the authenticated user, so guessing another account's photo ID gets nowhere.
Validated sharing
A share requires an email that belongs to a registered user and isn't the owner's own. Serializers validate all input, including unique usernames and emails and password strength.
Tested at the API
Authentication uses JWTs through Simple JWT, passwords use Django's hashing, and a Django APITestCase suite covers integration and security behaviour.